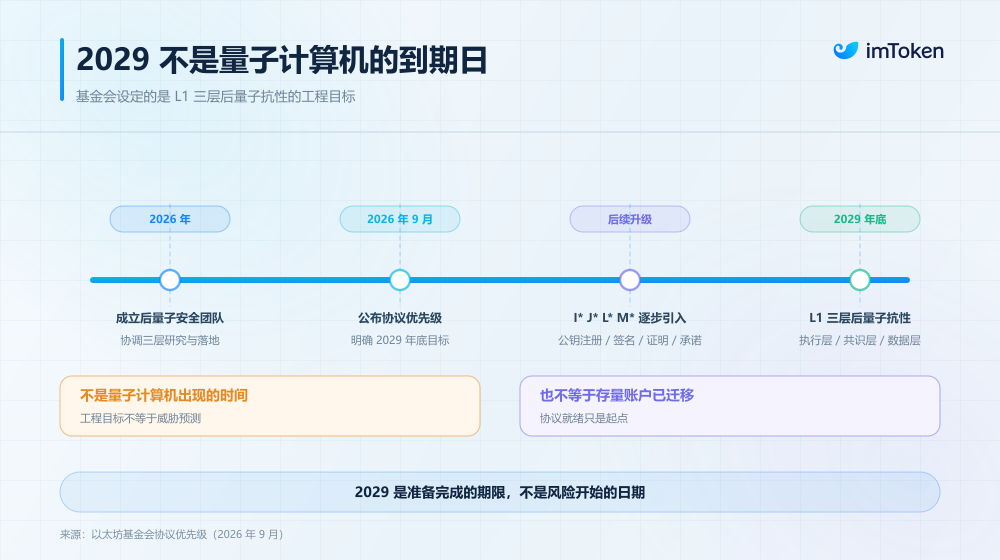
As reported on November 19, 2026, Ethereum’s post-quantum work was a long-term engineering effort, not an activated protocol upgrade or a response to a quantum computer already capable of breaking its cryptography. The report said the Ethereum Foundation had formed a Post-Quantum Security team and, in protocol priorities published that September, set a December 2029 target for quantum resistance across Ethereum L1’s execution, consensus and data layers. That date was a goal, not a guarantee.
The challenge extends beyond choosing a replacement signature. Ethereum must consider how existing accounts, validator votes and data commitments would keep working—and how users could retain control of assets while their authorization methods change.
Different components face different risks
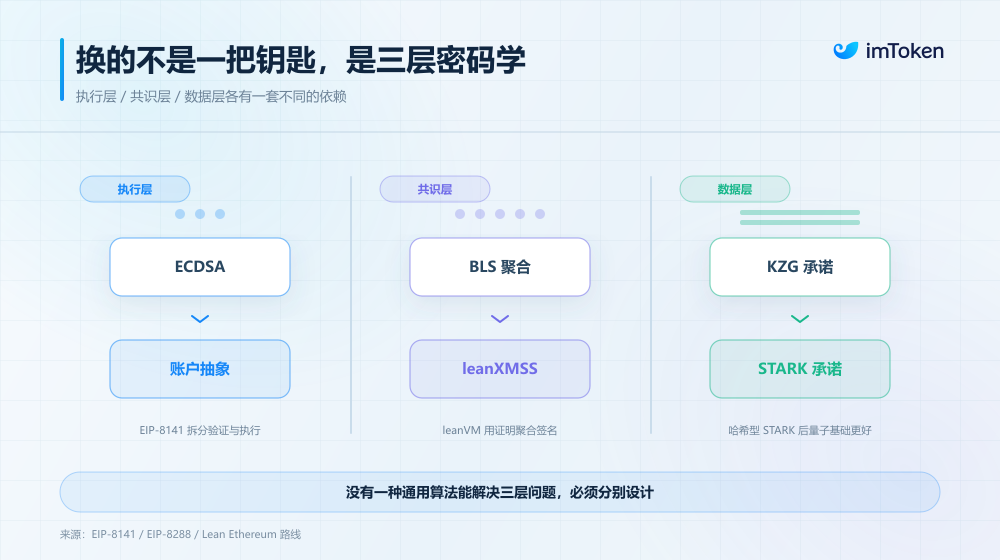
Ordinary externally owned accounts use ECDSA signatures. Ethereum’s proof-of-stake consensus uses BLS signatures, whose aggregation helps handle votes from a large validator set. KZG commitments support blob and Rollup data availability, while some application-layer zero-knowledge proof systems also rely on elliptic-curve assumptions.
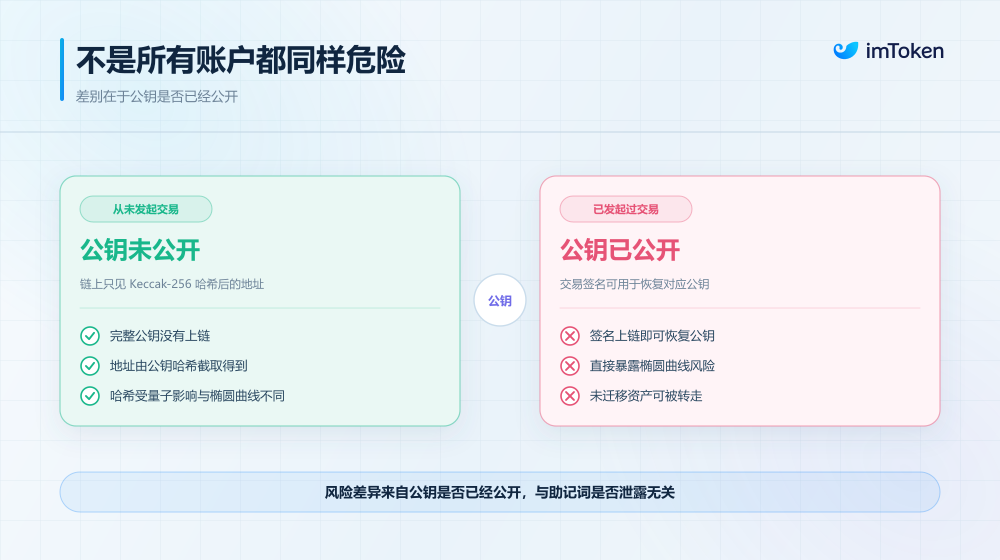
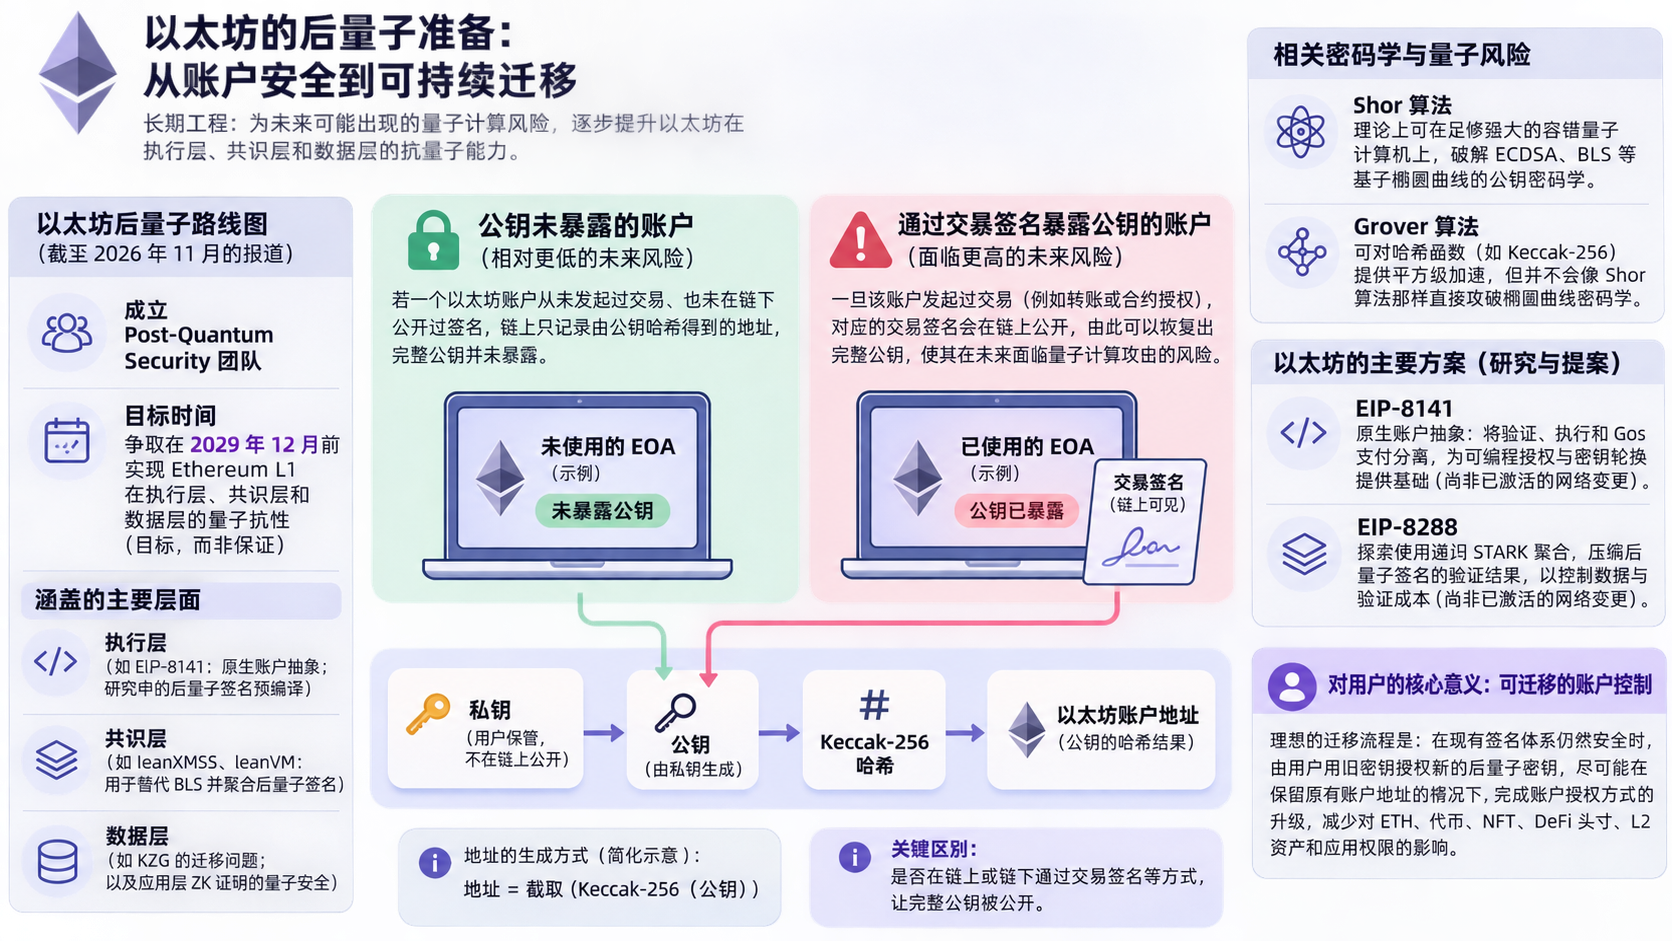
In theory, a sufficiently capable fault-tolerant quantum computer running Shor’s algorithm could undermine the public-key cryptography behind ECDSA and BLS. The report emphasized that no computer with that cryptographic-breaking capability existed at the time. Hash functions such as Keccak-256 face a different quantum risk: Grover’s algorithm offers a quadratic speedup, rather than the same kind of attack on elliptic-curve cryptography.
Exposure also differs among accounts. An ordinary Ethereum address is derived from a hash of its public key. If an account has never made a transaction or otherwise disclosed a signature, its full public key may not be public. A transaction signature, including one used for a contract approval, can reveal that key. This distinction matters when assessing a future attack; it is not a reason for users to move assets in haste.
Proposals across execution, consensus and data
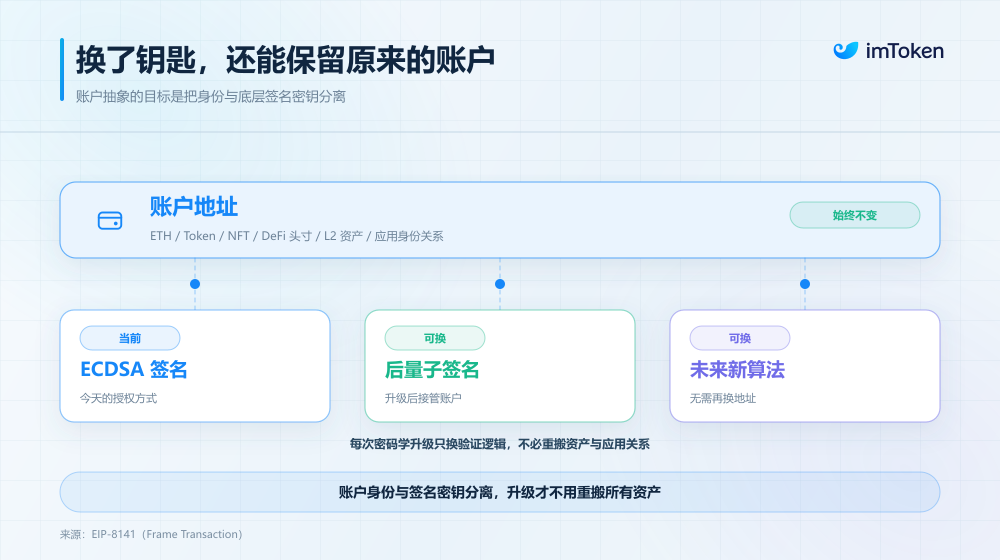
On the execution layer, the report discussed EIP-8141 as a native account-abstraction proposal. Its approach separates transaction validation, execution and gas payment, creating room for programmable authorization rather than permanently tying account control to one ECDSA key. That could support key rotation and, in some account designs, help users retain an address while changing how it is authorized. It does not mean existing accounts have already gained that capability. Post-quantum signature-verification precompiles were also described as an area of research.
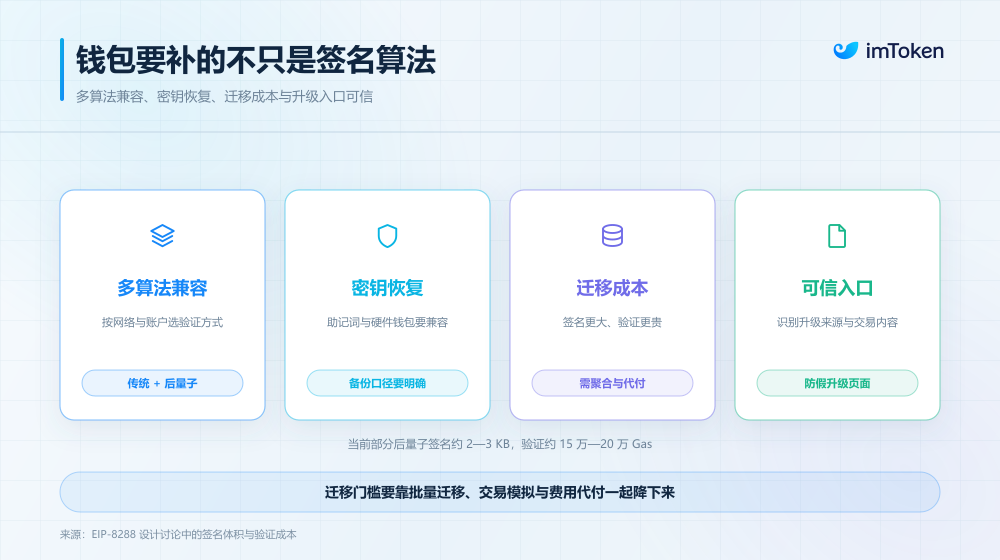
Larger post-quantum signatures would create data and verification costs. EIP-8288, another proposal cited in the report, explores recursive STARK aggregation to compress verification results. Neither proposal should be read as an activated network change.
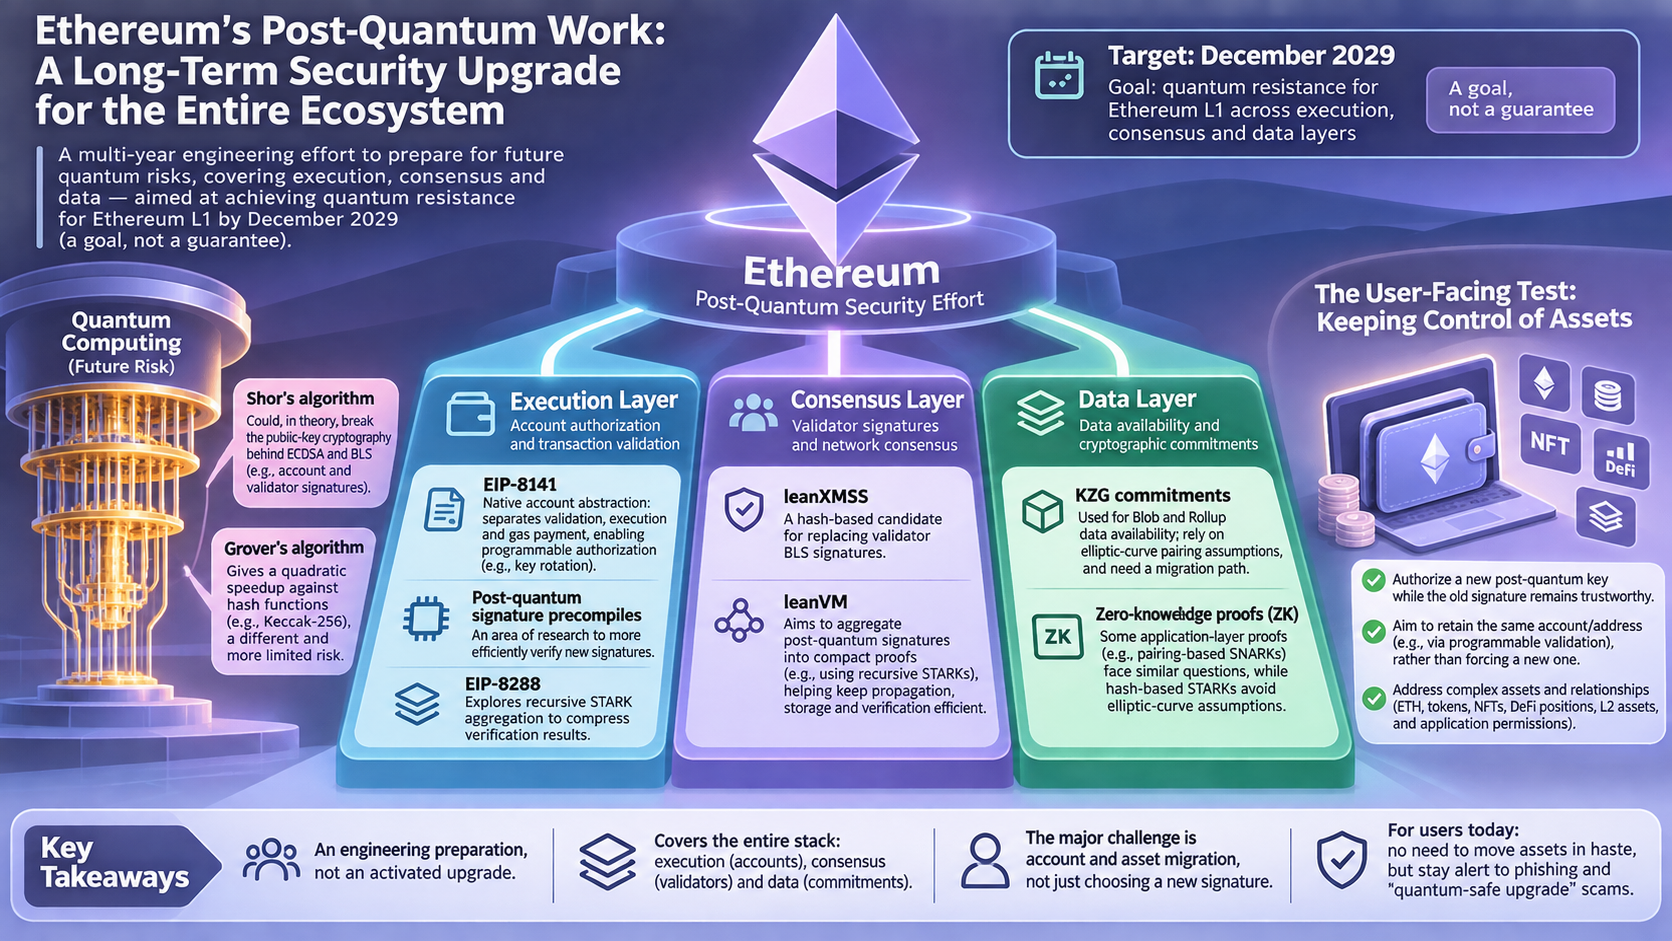
For consensus, the Lean Ethereum directions described in the report include leanXMSS, a hash-based candidate for replacing validator BLS signatures, and leanVM, intended to help aggregate post-quantum signatures into compact proofs. Simply substituting larger signatures for BLS would otherwise put pressure on peer-to-peer propagation, storage and verification.
The data layer presents a separate migration problem because KZG commitments depend on elliptic-curve pairing assumptions. Some pairing-based SNARKs used by applications face related questions; hash-based STARKs avoid reliance on elliptic-curve discrete-log assumptions. Any transition would therefore reach beyond L1 into Rollups and other applications.
Account control is the user-facing test
For a conventional account, adopting a new key system could mean moving to a new address. That is more complicated than transferring ETH: tokens, NFTs, DeFi positions, L2 assets and application permissions may all be associated with the old address. Programmable account validation offers a possible way to separate account identity from the key that controls it, but the migration path remains consequential.
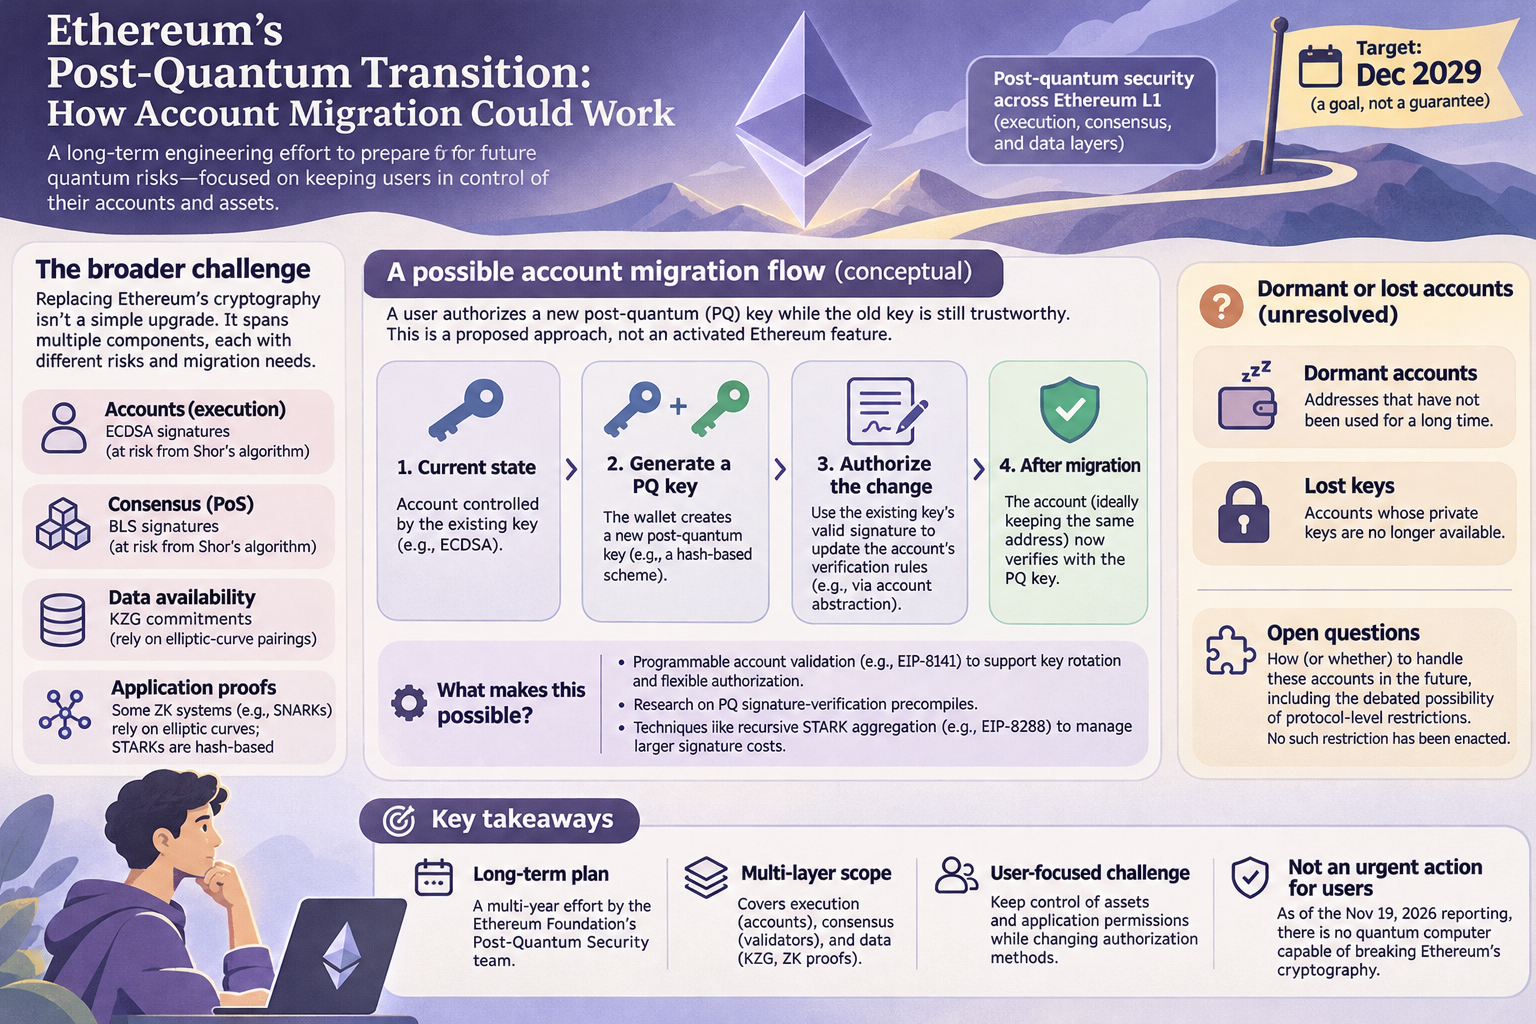
The report described a preferred sequence in which a user authorizes a new post-quantum key while the old signature remains trustworthy. If an attacker could already forge signatures from the old key, that authorization alone would no longer establish who owned the account. Dormant accounts and lost keys pose unresolved questions, including the disputed possibility of future protocol-level restrictions. No such restriction was reported as enacted.
Wallets would also need to make any eventual migration understandable and verifiable. A purported “quantum-safe upgrade” page could instead be a phishing attempt seeking a seed phrase or malicious approval. As of the original November 2026 reporting, the practical message was preparation by protocol and wallet developers—not an urgent instruction for users to migrate assets.